
Hunting Logic Flaws: Exploiting Multi-Step Workflows
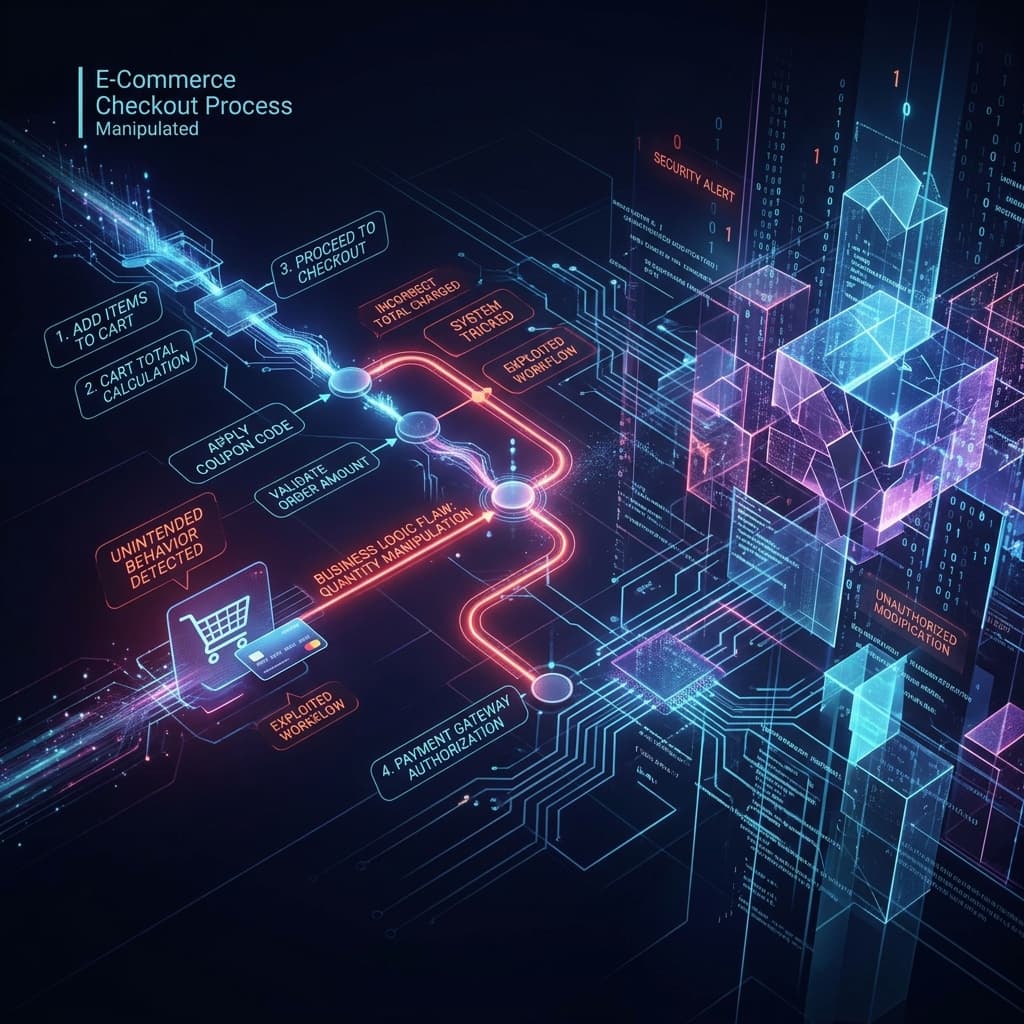

Imagine you're testing an e-commerce application. You add a $2,000 laptop to your cart. You proceed to the shipping page, enter your address, and apply a 10% coupon code. But right before you hit the final "Confirm Payment" button, you open a second tab, remove the laptop, and add a $5 sticker.
You go back to the first tab and hit confirm. The application charges your card $4.50 (the sticker price minus 10%), but the fulfillment backend processes the order ID that was originally tied to the laptop.
Congratulations, you just bought a laptop for less than a cup of coffee.
This is a business logic flaw, and automated scanners will never find it.
The Goal & Scope Rules
Business logic flaws exist because developers assume users will interact with an application sequentially (Step A → Step B → Step C). As a bug bounty hunter or penetration tester, your entire goal is to break that assumption. You want to skip steps, perform them out of order, or perform them simultaneously (race conditions).
Always ensure you are testing authorized targets, and never exploit logic flaws against real financial gateways using stolen cards or production funds. Always use the provided test credit cards (like Stripe's 4242 testing numbers) in authorized sandbox environments.
The Workflow: Breaking the Sequence
Hunting logic flaws requires a fundamental shift in how you use your proxy. If you rely entirely on automated tools, you are wasting your time. You have to manually map the application's intended state machine.
Stage 1: The Happy Path
First, walk through the application exactly as the developer intended. Buy a product, create a user, upgrade a subscription, or transfer funds. Record the entire flow in Burp Suite or Caido. You need to understand how state is passed between requests. Are they using hidden form fields, cookies, JWTs, or server-side sessions?
Stage 2: State Manipulation
Once you know the happy path, start dropping and replaying requests out of order.

Cybersecurity enthusiast focused on ethical hacking, penetration testing, bug bounty hunting, and security education. Founder of CyberBlockz, sharing practical cybersecurity knowledge, CTF challenges, and hands-on training to help learners develop real-world security skills and stay updated with the latest threats and vulnerabilities.

 An architecture diagram showing multiple concurrent API requests hitting a payment gateway before the database can update the ledger state.